

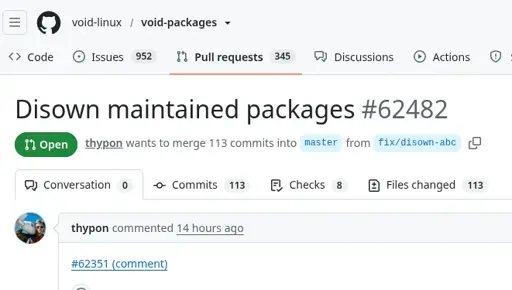
Cited from the article:
[…] the Void Linux project does have a contributing policy over AI usage that reads:
"In this section, “AI” refers to generative artificial intelligence tools, including Large Language Models and similar technologies.
All contributions are expected to be made by humans. AI tools may be used for research and learning, but all content in contributions must originate from and be understood by the contributor. This includes code, documentation, issues, security reports, pull request descriptions, and comments in all Void Linux community spaces.
ALL usage of AI tools MUST be disclosed.
Do not bring AI review tools into pull requests.
Usage of AI-powered human-language translation tools is acceptable to facilitate contributions across language barriers."
Distro package maintainers are different than software dev maintainers.
They mean no one can be reasonably be up to date on software security updates, and (ideally) ensuring all packages changes are not malicious (as well as the small stuff like properly integrating to the distro, but idk how void works enough to comment on that)
Cause like I can write a ton of guix configs that’ll probably run until the next ice age, but that does nothing about the dev who’s software I packaged, that now decided they’re personally god and need to spread christ as fast as possible.
(Also off topic but that’s the power and curse of nixos-like distros, its too easy to package so odds are the shit ain’t updated, and suddenly there’s 1000 Firefox packages in nixpkgs)
Some people do an astounding amount of work.
And then there are many, many, which help a little.
Also, if, say, somebody finds that in Debian testing is a malicious package, people which maintain Arch will learn that. Open information sharing between many thousands of people willing to coordinate is a superpower.
Oh god yeah, its just filtering through the slop that actually matters.
But like the XZ trojan that was only affecting Debian installs, each distro needs to individually have competent maintainers to ensure their store is safe.
If for exapmle I set a couple ‘bugfixes’ in the guix package file for emacs, I could reasonably infect a number of systems if a lazy maintainer just approved the request. (Or other attacks without even involving guix if I notied a bug in a package spelling and typo squatted it, or stole signing keys and pushed updates to the repo myself).
None of these would change anything to other distros maintainers, but because this distros AI maintainer could risk a large number of users devices.