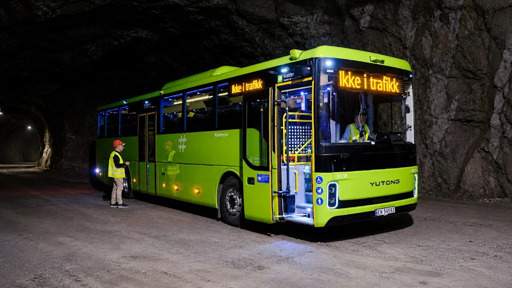
Researchers drove a NIO ES8 electric SUV deep into a Norwegian underground mine specifically to sever its external connections. The car kept attempting to reach servers, most of them located in China. These findings echo broader concerns about hidden data collection, similar to how a surveillance app was built to covertly target users without their knowledge.
That finding sits at the center of Project Lion Cage, a multi-year study initiated in 2022 by Tor Indstøy, a risk management and threat intelligence executive at Telenor Group. Indstøy purchased the NIO ES8 as a dedicated research platform.
The project arrives as Chinese EV brands expand across European markets with assurances about local data processing. Observed network behavior appears to contradict those assurances.
This article is so stupid with the dumbest fearmongering clickbait title -
Anything that calls home will try to call home. Connection or not. You put an removed in a faraday cage and it will try to phone home. There’s no reason it would suddenly stop doing that because there’s no point to adding another line of code to get it to stop when it doesn’t need to.
Not to mention that the important part is this:
Now compare that to a plethora of other car manufacturers that don’t even bother to encrypt your data and explicitly say that you will be tracked by them and have your data sold.
https://cybernews.com/privacy/mozilla-cars-track-sexual-activity-sell-data/
this. I seen people try to just use hostnames to block the LG telemetry, and the result is it just phone home harder, the logs just show it spams thousands of requests per second. Only way to stop it is to relay it to a fake server to return a fake response.